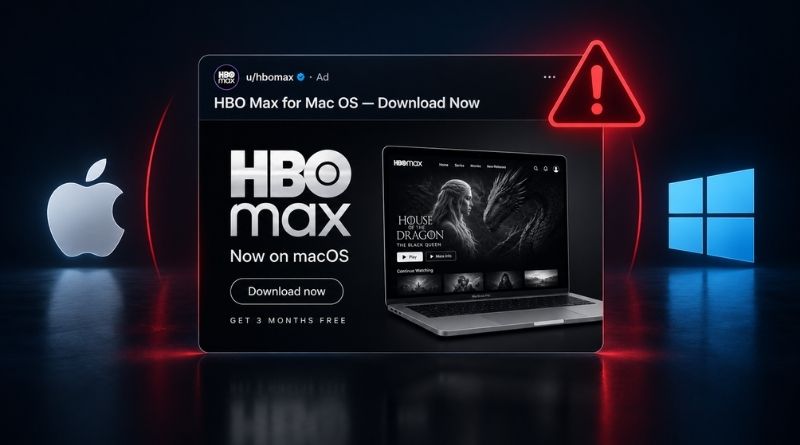
Cybercriminals have found another way to make malware attacks look trustworthy. HBO Max’s verified Reddit account was hijacked and used to promote malicious advertisements that could infect users’ devices.
According to cybersecurity researchers, the attackers published 108 malicious ads over around 48 hours. Because the ads came from a verified corporate account, they looked more believable and could easily make users lower their guard.
The campaign promoted fake AI tools, developer software, and macOS utilities. Some advertisements also directed users to websites designed to look like official HBO Max pages.
How the HBO Max Reddit Attack Worked
The fake websites claimed to offer an HBO Max app for Mac or a special promotional download. However, instead of providing normal software, the pages asked visitors to open Terminal on macOS.
Windows users were instructed to open the Run dialog or PowerShell. They were then told to copy and paste a command.
This technique is known as ClickFix. It tricks people into believing that they are completing a normal technical step, such as fixing an error, passing a CAPTCHA, or installing software.
The danger is simple: the victim ends up running the malicious command themselves.
Researchers have referred to the operation connected with these advertisements as “PasteSwitch.” The campaign can reportedly adjust its attack depending on the victim’s device and the type of advertisement being shown.
Malware Used in the Campaign
| Platform | Reported Threat | Potentially Targeted Data |
|---|---|---|
| macOS | MacSync and AMOS | Browser data, passwords, Telegram data and crypto information |
| Windows | Amatera | Sensitive information stored on the device |
| Both | Clipboard hijackers | Cryptocurrency wallet addresses |
Why ClickFix Attacks Are Dangerous
ClickFix attacks work because they focus on human behavior rather than simply exploiting a technical weakness. A website may tell users that something has gone wrong and provide a quick solution.
The instructions can appear professional and urgent. Some campaigns may even use countdowns or fake user numbers to pressure visitors into acting quickly.
That is why a verified account should not automatically be treated as proof that an advertisement is safe.
How to Stay Safe
Users should avoid downloading software directly from advertisements, even when those ads appear under trusted brand names. Instead, go directly to the company’s official website.
Never paste commands into Terminal, PowerShell, or the Run dialog simply because a webpage tells you to do so. If a website asks for this, stop and verify the instructions through official documentation.
Keeping your operating system, browser, and security software updated can also provide an additional layer of protection.
Most importantly, slow down. A few extra seconds of checking can prevent a serious malware infection.
Final Thoughts
The HBO Max Reddit account hijacking shows why online trust can be easily abused. A familiar brand name and a verified account can make a malicious advertisement look legitimate.
ClickFix campaigns continue to rely on this type of social engineering. Staying cautious, avoiding unknown commands, and downloading software only from trusted sources remain some of the simplest ways to reduce the risk.